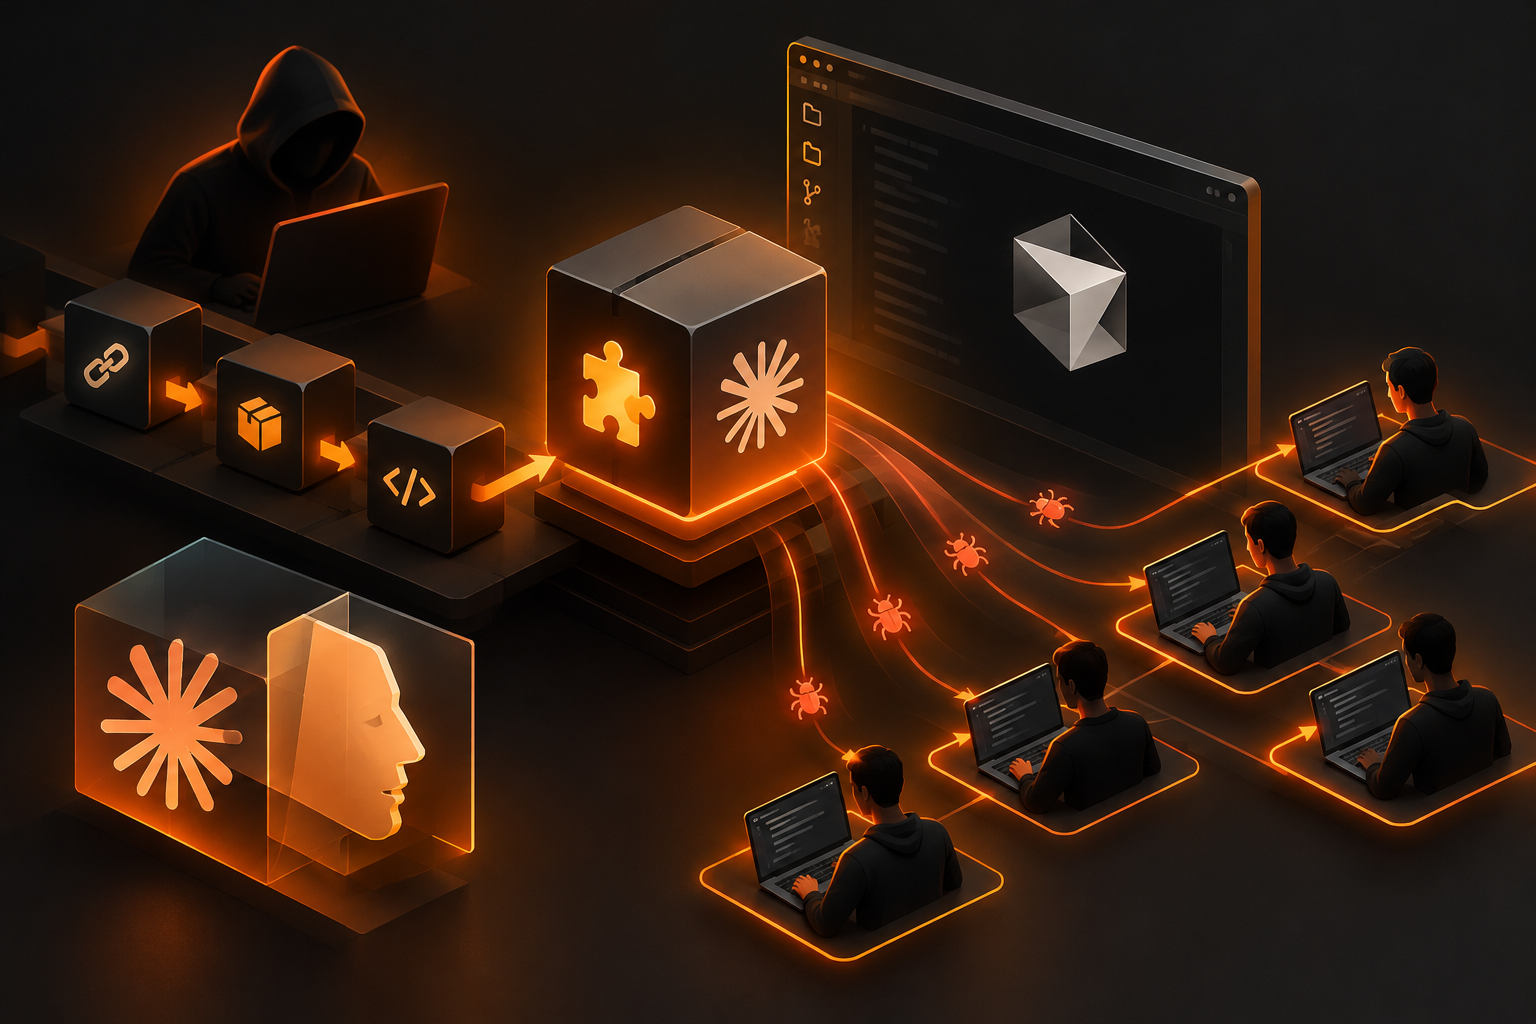
If you installed the Claude Code extension for Cursor in recent days, check which version is running. According to The Decoder, a tampered version was available in Cursor's VS Code extension marketplace on Thursday for about eleven hours. Cursor names up to 5,000 affected users. According to the company, Anthropic was not involved in developing it.
What the extension was meant to do
According to Cursor, the extension tried to collect hostname, username, operating system and public IP address, and to set up remote access for the attacker. Ars Technica additionally reports an attempt to establish a persistent SSH backdoor. Cursor itself says this step would likely have failed on most machines without administrator rights.
Response and open questions
Cursor removed the version and took the marketplace offline temporarily; according to the company, it was brought back online after the malware was neutralized. Cursor says no other extensions were affected. According to Ars Technica, it is still unclear how attackers gained access to Anthropic's verified account in the marketplace, and at the time of reporting Anthropic had not yet issued a public warning to customers.
What you can do now
Anyone who installed or updated the extension within the stated time window should have their machine checked and verify the version number. Ars Technica also recommends turning off automatic extension updates in Cursor if you can configure that in the settings.
Sources
Editorially owned by Ideal Syka. Sources and method: Newsroom & method. Tips and corrections: ai@i6eal.de.